90% of AI Code Contains Vulnerabilities: How to Verify Code After Vibecoding
Cursor wrote your login form. It works. But it contains an SQL injection, a hardcoded API key, and an endpoint with no authorization check. A joint study by CMU, Columbia University, and Johns Hopkins University (2025) found: 90% of code generated by AI assistants contains potential security vulnerabilities. This doesn't mean AI code can't be used — it means it can't be deployed without review.
Key facts
- 90% of AI-generated code contains vulnerabilities per CMU/Columbia/Johns Hopkins (2025)
- Automated tools catch 30–50% of issues — the rest require a human
- AI review doesn't find bugs in AI code: same training data, same blind spots
- Code review against spec + security audit costs $300 one-time or from $50/month
During rollout planning for vibers-code-review, the recurring issue was not feature quantity but whether a buyer could verify limits, exports, integrations, and ownership before committing.
Why Does AI Generate Vulnerable Code?
Because it was trained on GitHub — which has massive amounts of insecure code. The most frequent pattern in training data is not the most secure one. AI is optimized for "it works" — security must be explicitly requested, and even then results are not guaranteed.
Types of Vulnerabilities
SQL Injection (CWE-89) AI inserts user input directly into queries:
# AI generated:
query = f"SELECT * FROM users WHERE name = '{user_input}'"

# Should be:
cursor.execute("SELECT * FROM users WHERE name = %s", (user_input,))
XSS — Cross-Site Scripting (CWE-79) AI inserts content without escaping:
// AI generated:
element.innerHTML = userComment;

// Should be:
element.textContent = userComment;
Hardcoded Secrets (CWE-798) AI copies patterns from training data, including API keys:
// AI generated:
const API_KEY = "sk-proj-abc123...";

// Should be:
const API_KEY = process.env.API_KEY;
Missing Authorization (CWE-862) AI creates endpoints by analogy but forgets permission checks:
// AI generated:
app.delete('/api/users/:id', async (req, res) => {
  await db.users.delete(req.params.id);
  res.json({ success: true });
});

// Should be:
app.delete('/api/users/:id', authMiddleware, async (req, res) => {
  if (req.user.role !== 'admin') return res.status(403).json({ error: 'Forbidden' });
  await db.users.delete(req.params.id);
  res.json({ success: true });
});
Path Traversal (CWE-22) AI processes file paths without validation:
# AI generated:
filepath = os.path.join(UPLOAD_DIR, filename)
# filename can be "../../etc/passwd"

# Should be:
filepath = os.path.join(UPLOAD_DIR, os.path.basename(filename))
AI Code Verification Checklist: What to Check and When?
Use this list before every release and on every PR containing AI-generated code.
Critical Checks (always do)
- [ ] User input — is everything escaped/validated before use?
- [ ] SQL queries — are parameterized queries used?
- [ ] Secrets — are there API keys, passwords, tokens in code?
- [ ] Authorization — does every endpoint check permissions?
- [ ] File operations — are paths validated?
- [ ] HTTPS — are all external requests over HTTPS?
Important Checks (do before release)
- [ ] Rate limiting — is the API protected from brute-force?
- [ ] CORS — configured correctly (not
*)? - [ ] Logging — are secrets not being written to logs?
- [ ] Dependencies — are there deprecated or vulnerable packages?
- [ ] Error handling — does stack trace not leak to users?
- [ ] Session management — are tokens stored securely?
Business Logic Checks (do on every PR)
- [ ] Spec compliance — does code do what was asked?
- [ ] Edge cases — empty input, null, negative numbers?
- [ ] Parallel requests — are there race conditions?
- [ ] Rollback — what happens on error mid-operation?
Tools: What They Catch, What They Miss
Automated (catch 30-50% of issues)
| Tool | What it does | Price |
|---|---|---|
| ESLint Security Plugin | Basic vulnerability patterns in JS/TS | Free |
| Bandit | SAST for Python | Free |
| npm audit / pip audit | Dependency vulnerabilities | Free |
| DeepSource | AI SAST + autofix | $12/user/mo |
| SonarQube | Comprehensive static analysis | Free (self-hosted) |
AI Review (catch 50-70% of issues)
| Tool | What it does | Price |
|---|---|---|
| CodeRabbit | AI comments on PRs | $12/user/mo |
| Copilot Review | Built-in AI review | $19/mo (with Copilot) |
Human Review (catch 85-95% of issues)
| Tool | What it does | Price |
|---|---|---|
| Vibers | Spec-based review + PRs with fixes | from $50/mo |
| PullRequest.com | Expert review | $50+/hr |
| Hiring a senior | In-team review | $50-150/hr |
Why Automated Tools Are Not Enough
Automated tools search for known patterns. They'll find innerHTML = userInput because it's in their rule database.
They won't find: - Business logic that allows zeroing price through a discount - An API endpoint accessible without auth because AI copied it from an internal service - A payment flow that doesn't verify 3D Secure - A race condition in payment processing allowing double charges
These issues require context understanding — which no automated tool has.
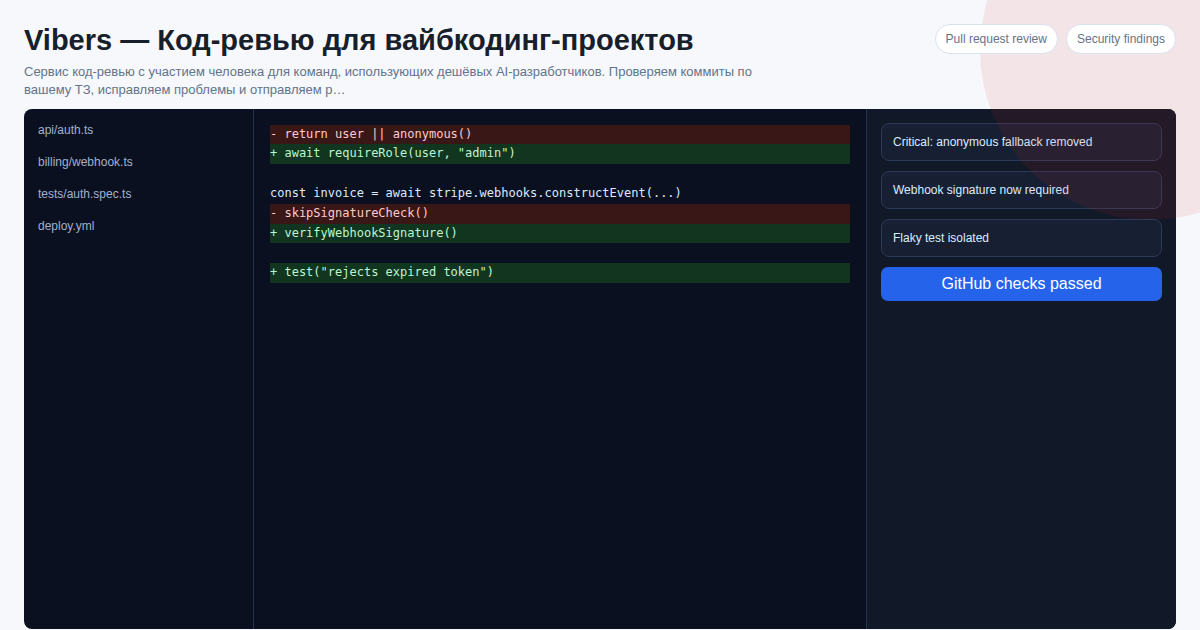
How Vibers Reviews AI Code Against Your Spec
- Add
marsiandeployeras collaborator to your GitHub repo - Send your spec — Google Doc, Notion, PDF
- We review every commit — security + spec compliance + AI hallucinations
- Send PRs with fixes — not a report, working code
| Category | Examples |
|---|---|
| Security | OWASP Top 10, secrets in code, authorization |
| Hallucinations | Non-existent APIs, deprecated methods, fabricated packages |
| Spec compliance | Feature does what was asked, nothing missing |
| Business logic | Edge cases, race conditions, error handling |
| Visual/UI | Broken layouts, mobile issues, wrong colors |
Code review costs $300 per project. Write on Telegram: @onoutnoxon — we'll check your code for vulnerabilities.
FAQ
Is this page updated for 2026? Yes. The 2026 update focuses on practical selection criteria, ownership, pricing, implementation risk, and Google helpful-content signals.
When should I choose a custom solution instead of a SaaS tool? Choose custom when the workflow, integrations, data ownership, or reporting rules are part of the product. Use SaaS for quick validation.
How should I use "90% of AI Code Contains Vulnerabilities: How to Verify Code After Vibec…" before buying? Treat it as a checklist: compare cost, limits, migration effort, support model, and whether the vibers-code-review scenario matches your real process.
Sources
- https://onout.org/90-procentov-koda-ot-ii-uyazvimy
- https://developers.google.com/search/docs/fundamentals/using-gen-ai-content
- https://developers.google.com/search/docs/fundamentals/seo-starter-guide
This vibers-code-review guide uses AI-assisted drafting and human editorial review by Alexander Ruin, founder of onout.org. Updated: 2026-05-01.
About the service "90% of AI Code Contains Vulnerabilities: How to Verify Code After Vibecoding 2026"
CMU research shows 90% of AI code has vulnerabilities. Checklist for verifying code from Cursor, Copilot, ChatGPT. How to protect your project from AI bugs.